2015 · Environment and bindings
Review site gates without broadening authority
Turn the four explicit deployment requirements into a scoped readiness checklist while preserving all false and unknown states.
Open a workspace beside this lesson. Protected links keep their existing access gates; no new permission is granted by this course.
Why this matters
Ordinary design publication and physical/cloud operation are separate permissions.
Missing deployment evidence should block dependent actions without suppressing safe source inspection.
Read the screen with the explanation
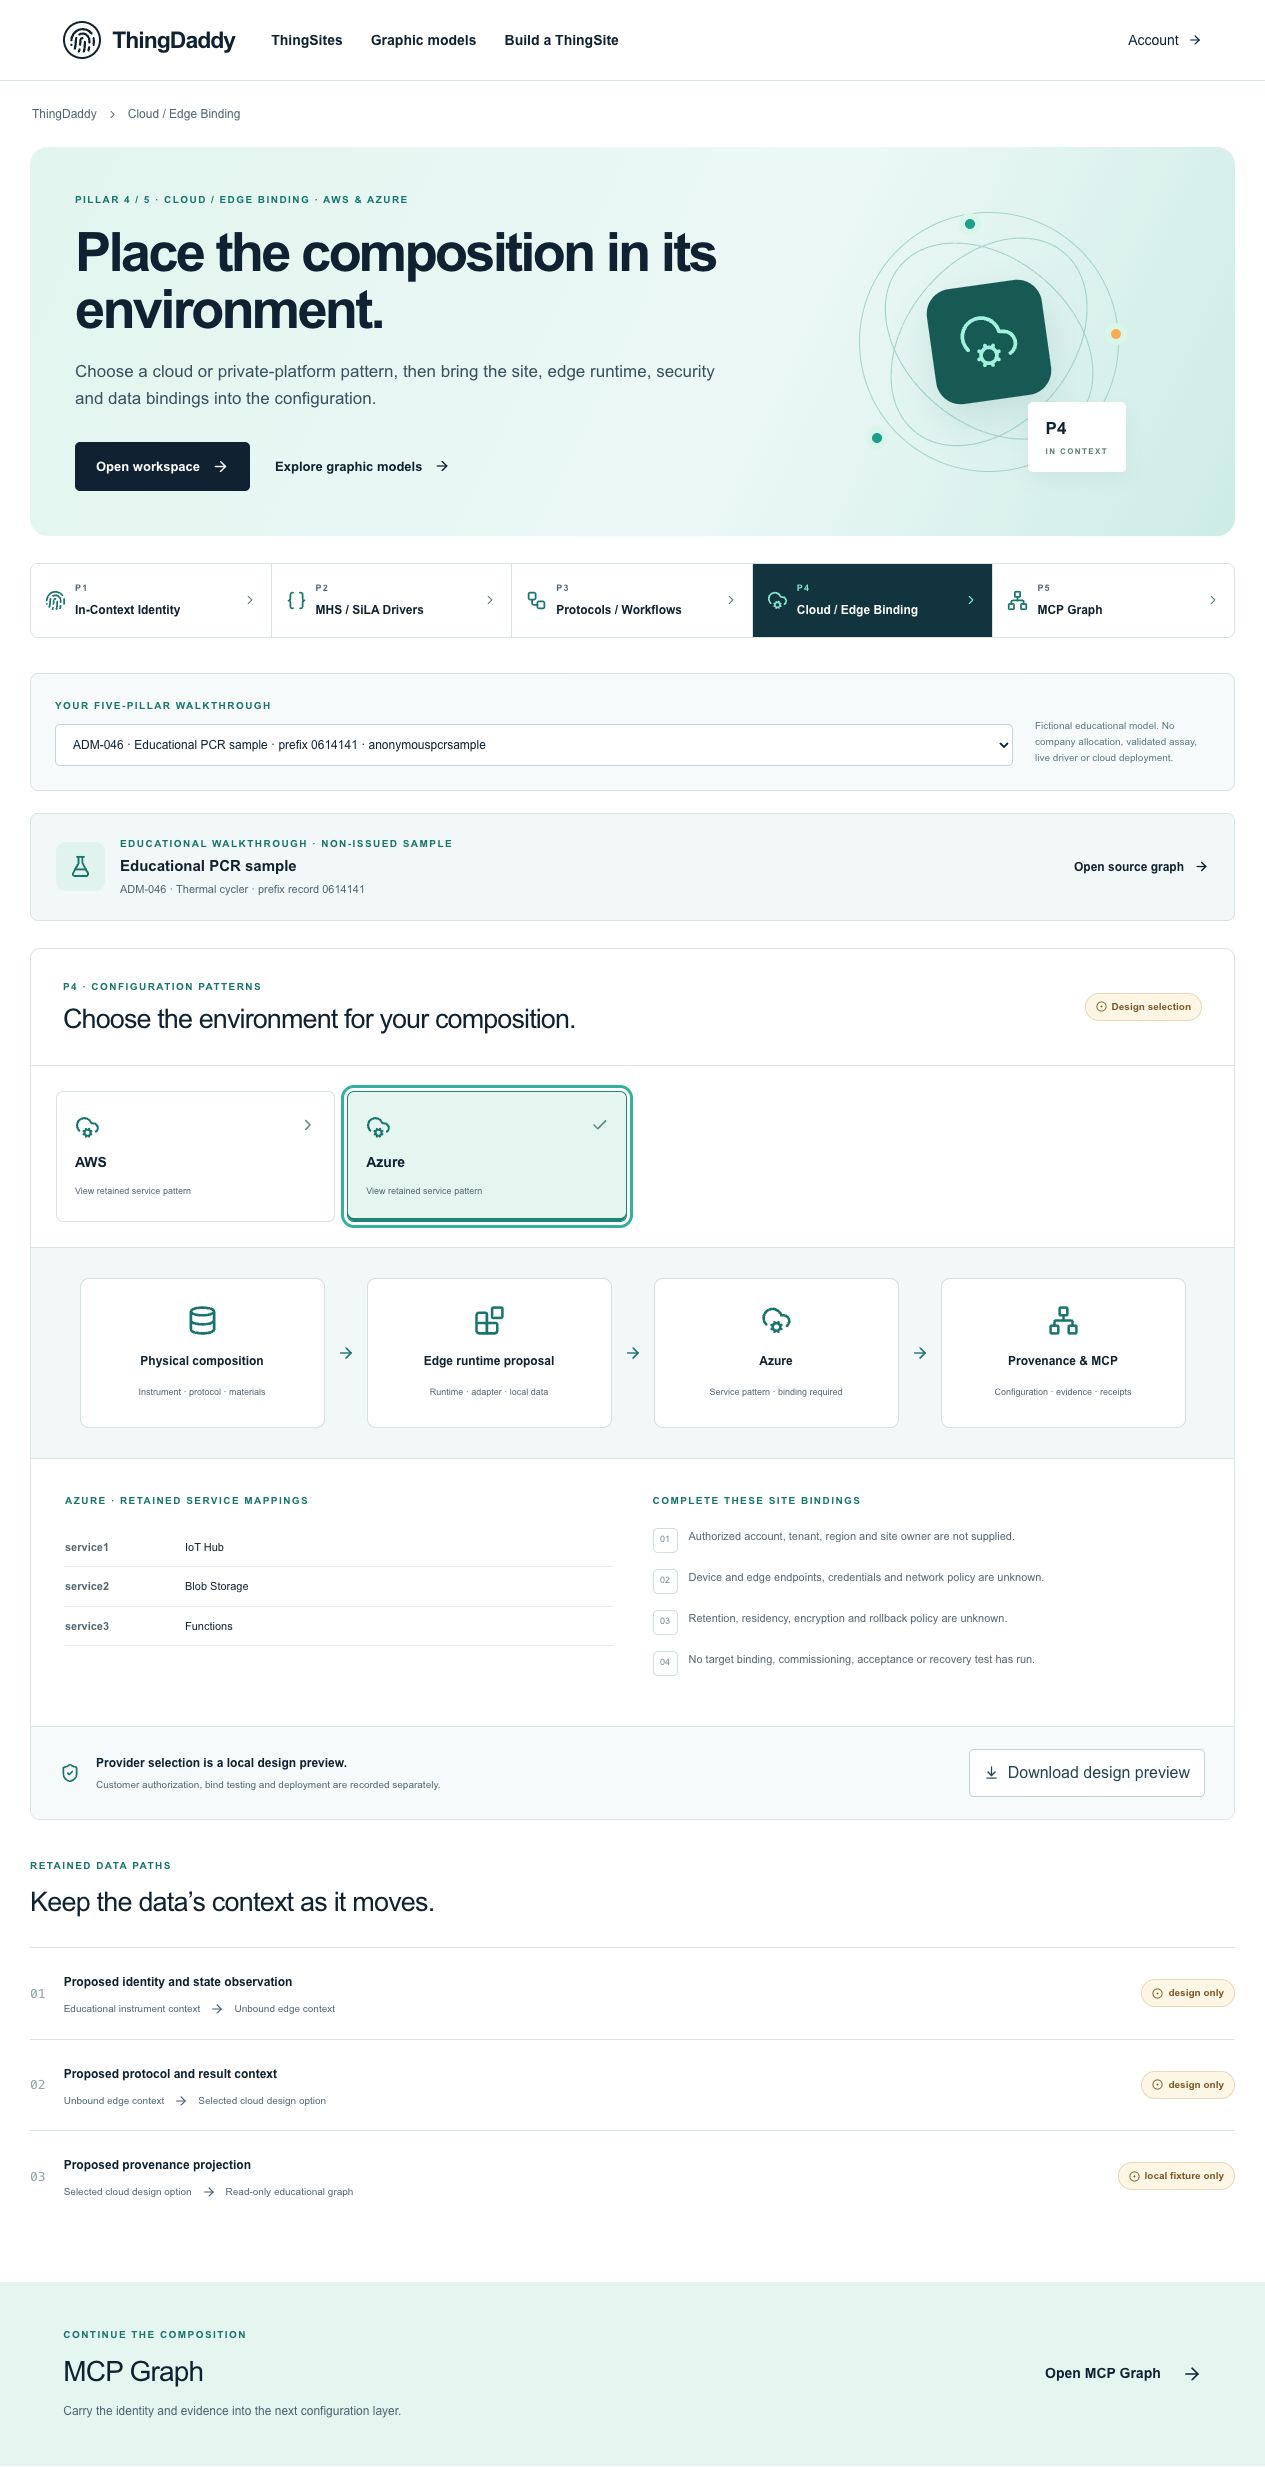
Earlier anonymous demonstration capture · Earlier local anonymous educational preview; not current physical execution or hosted acceptance · not evidence that this exercise has been performed. Open the image for full resolution.
Screenshot provenance
SHA-256 e897b41b24f298e057536a07afd979c64c9ed57339caa5cf6be28e33f81a93a1Captured 2026-10-13T05:14:16.647Z. Source-package pin: 2f78a982141bda51ba64ea8ccb3a07f527eec3f77cf89baaa1f05c102197f6fd. Original screenshot bytes preserved.
Step by step
01 Read the site requirements
Screen or control: Complete these site bindings
Why: A provider choice is insufficient operating context.
How: Open P4 and read all four numbered requirements without skipping the account/tenant/region/site-owner row.
What you should see: Missing authority, device/edge endpoints, policies and acceptance/recovery testing are explicit.
Verify: Copy each requirement into a separate checklist row and preserve the original wording and scope.
02 Inspect the exact gate data
Screen or control: Public package link · P4 deploymentGates
Why: The machine-readable gate must match the visible warning.
How: Open the public package and inspect #/P4/deploymentGates including gateResult and all four boolean states.
What you should see: gateResult is blocked and every authorization/deployment boolean remains false.
Verify: Record exact values rather than treating a visible warning as the only gate evidence.
03 Assign evidence needs, not fictitious approvals
Screen or control: Requirements list · Design preview evidence strip
Why: A readiness plan should say what is needed and who must authorize it.
How: For each row, name the evidence needed and its future reviewer scope in your exercise notes. Do not enter secrets into this read-only sample.
What you should see: The plan remains an evidence request; the source still records missing bindings.
Verify: An imagined reviewer or a platform-owner preference is not authority evidence for a real customer or cloud account.
04 Confirm safe inspection remains available
Screen or control: Open exact design graph · Complete graph JSON
Why: A blocked dependent action should not hide the underlying evidence.
How: Open the selected design graph and inspect/export its original public source context.
What you should see: The source remains retrievable despite blocked deployment state.
Verify: Confirm there is no deployment success or execution receipt; unrelated read-only work can continue.
What is happening under the surface
The source gateResult is blocked because authorized site/account context, endpoints, policies and testing evidence are missing.
customerAuthorized, resourcesCreated, deploymentValidated and executionAuthorized are all false.
The public page supplies a review view, not forms to submit credentials, approve commissioning or deploy resources.
Common mistakes
- Do not treat site-owner approval as automatic company or vendor authority.
- Do not enter credentials into a teaching exercise.
- “Blocked deployment” does not mean the evidence should be hidden or merged away.
The records an agent needs
The source requirements distinguish authority, runtime/network binding, operating policy and verification. Marking one requirement planned does not make any gate true. The lesson performs no credentials submission, provisioning or physical dispatch.
Exact retained identities
urn:epc:id:gdti:0614141.00401.1urn:epc:id:gdti:0614141.00402.1Anonymous package occurrence pointers
#/P4/deploymentGates#/P4/deploymentGates/unresolvedRequirements#/authority#/boundariesFields or record paths to inspect
gateResultcustomerAuthorizedresourcesCreateddeploymentValidatedexecutionAuthorizedunresolvedRequirementsPointers locate records; hashes pin bytes; lesson numbers locate teaching material. None substitutes for an applicable assigned GS1 identity.
Apply what you learned
Create a four-gate readiness matrix with unknowns and scoped next actions.
Prepare these outputs
- One row per original unresolved requirement with its exact source pointer.
- Needed evidence, responsible reviewer role and dependent action.
- The current false/unknown gate values copied unchanged.
Review your work against these checks
- No approval or validation is invented.
- The matrix distinguishes content publication from operational execution.
- All original read-only source records remain accessible.
Check your reasoning
A provider is selected but site/account authority and binding tests are absent. What is the safe next step?
This answer stays in page memory, is cleared when you leave, and is not sent or recorded as certification, validation or authority.Source and current boundaries
Screen basis: the anonymous public educational fixture at /api/demo/pillars, namespace 0614141. No private company record is read by this course.
Pinned assessed package SHA-256: b06ee255d0943a048511092595db4b98281b9b761d1910d19e6c3dba82591d94. Its complete graph contains 329 nodes and 231 directed relationships; original excluded assertions remain separately retained provenance. Lesson locators are educational numbers, not issued GS1 keys.
Scope: fictional authored records, non-issued identity proposals, unknown authority, no physical command, assay validation, cloud deployment or execution authorization.
fictional authored, non-issued, read-only
b06ee255d0943a048511092595db4b98281b9b761d1910d19e6c3dba82591d94Open primary referenceReading, answering a question and opening a diagram do not issue identifiers, validate a scientific method, establish company authority, commission an environment or authorize physical action.